
18+ years across four major banks, defence and government · Author, The CISO's AI Firewall
Board-level security and AI leadership for organisations navigating cyber risk, AI adoption and regulatory change.
18+ years across four major banks, defence and government · Author, The CISO's AI Firewall
Through our delivery partner
Cyber Arista
01 / YOU ARE PROBABLY HERE BECAUSE
Your CISO resigned without notice. The accountability for security did not leave with them.
02Staff are already using AI tools across the business. Nobody has been given ownership of the risk.
03A tender or contract now requires ISO 27001, and there is a date to work back from.
04The audit or assessment report has landed. Now it needs a named owner and a credible plan.
05Your cyber insurance renewal is approaching, and the insurer wants evidence, not assurances.
06The board asked who is accountable for AI, and that deserves a better answer than silence.
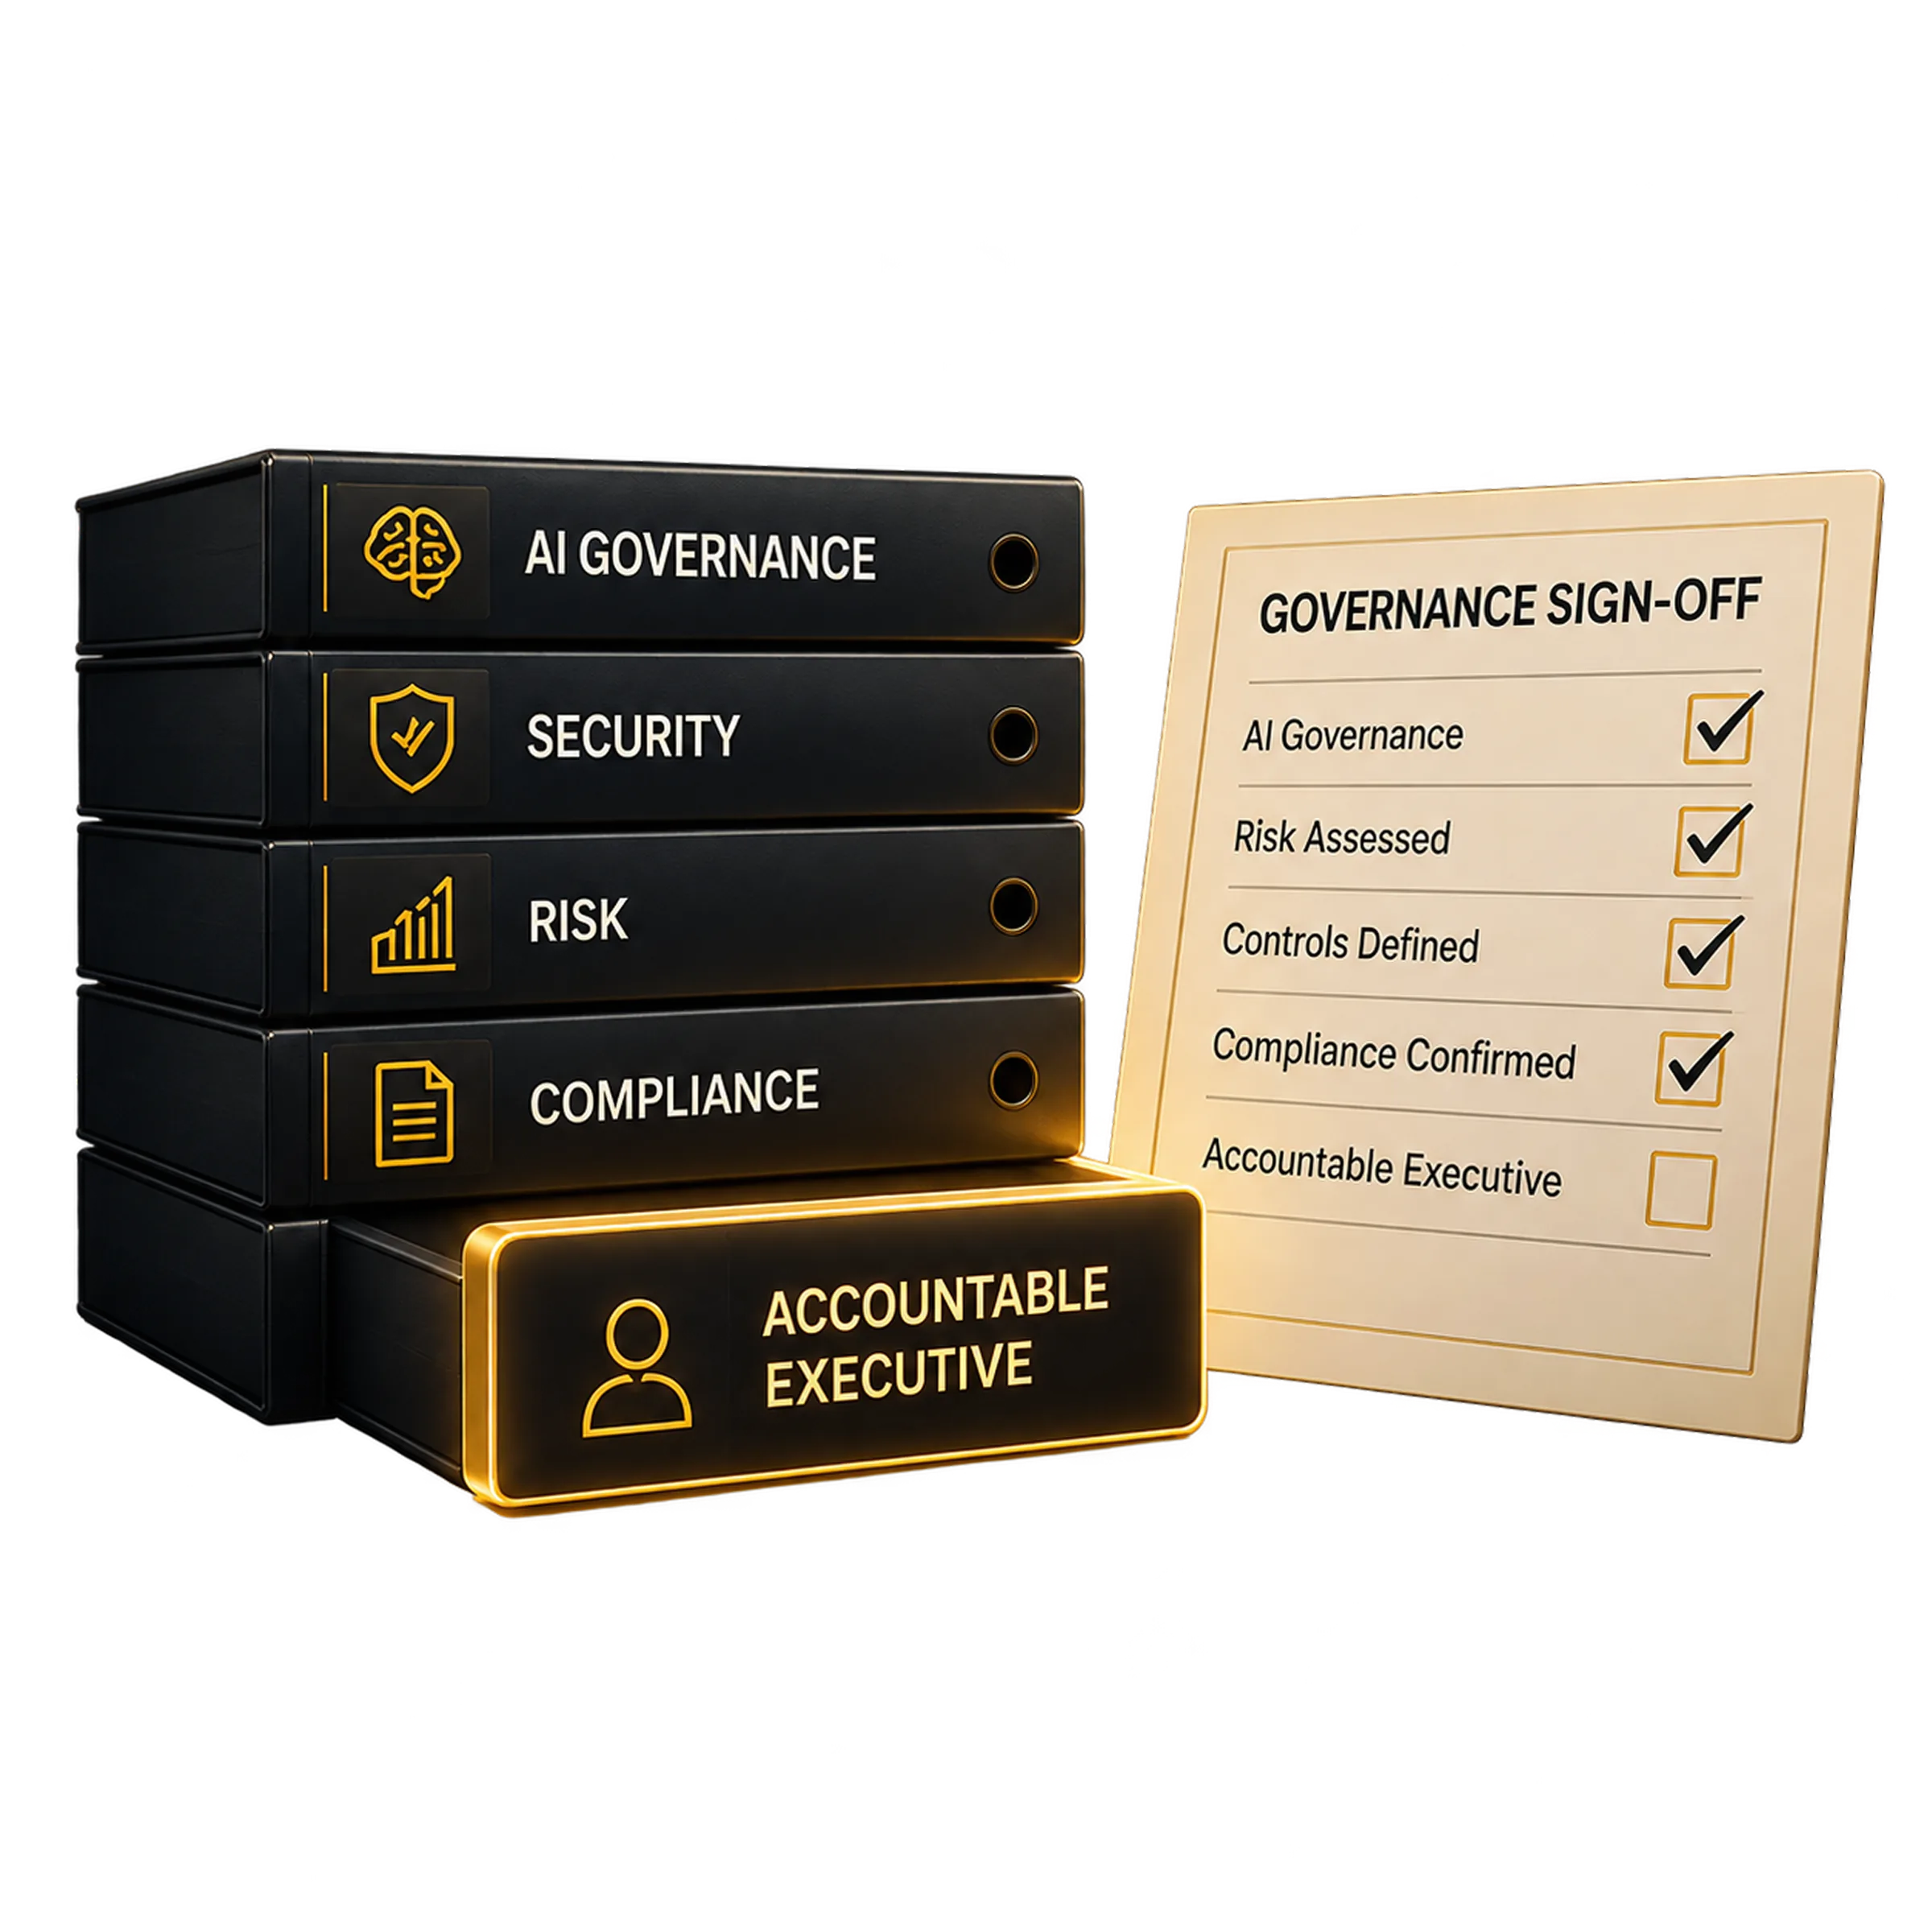
Security baselines are being rewritten faster than certification cycles complete.
Each regime moves on its own clock: in force in some markets, phasing in elsewhere, principles-based in others. Even the deadlines have moved.
AI reached the workforce before it reached the org chart. Very few organisations have named an executive accountable for it.
And will your compliance still hold when the rules move again?
AISF, the Cybersecurity Link AI Security Firewall, turns your AI policy into controls that run where your models, agents and MCP tools run, and keeps the evidence to prove it. It is the method from The CISO's AI Firewall, built as a platform.
The rules moved, and AI is already in production. A policy on paper doesn't stop an agent calling a tool it shouldn't.1,000+ AI policy initiatives across 69 countries, territories and the EU (OECD.AI).
Write AI policy once, as code, with approvals and version history.
Find every model, agent and MCP server, and map its attack paths.
Apply policy inline: audit first, then simulate, then enforce on routes you approve.
Assume a detector can miss. Limit what an AI system can reach and do.
Every decision recorded and mapped to ISO 42001, NIST AI RMF and OWASP.
AISF launches as SaaS and as a virtual appliance. A hardware appliance follows once the software has run in production with our design partners. It is the same product throughout, so nothing you configure in the first release has to be rebuilt later.
The quickest start. Point your AI traffic at the gateway and use the hosted console.
Runs in your environment, so AI traffic and prompts stay inside your boundary.
The same software on certified partner hardware, for sites that need a dedicated box.
You set data handling per tenant and can change it per route. It answers the CISO's first question: what can Cybersecurity Link actually see?
Only metadata leaves: decisions, IDs, timings.
Highest sensitivitySensitive elements masked before storage.
SaaS defaultFull content, encrypted under keys you manage.
Forensic replayContent never leaves your environment.
Virtual · hardwareWe are taking on 3 to 5 organisations to pilot AISF on their real AI estates. Partners get early access, a seat on the roadmap and direct access to the architect. We won't use your logo without written consent.
Independence. AISF is a separate product line. Our advisory and assessment work stays product-neutral: we never make AISF a condition of an engagement or recommend it as a finding in our own assessments.
Status. AISF is in development. This section describes the planned release. AISF reduces AI attack paths and limits blast radius. It does not claim complete prevention or automatic compliance, and it is not IRAP-assessed.
03 / TWO EXECUTIVES
Your security executive. Strategy, governance, risk, board reporting and crisis leadership, held by a named senior practitioner, not a platform.
Your AI executive. Accountable for AI strategy, governance, risk and security, with the technical depth to red-team the systems it governs.
04 / ECONOMICS
The right answer when the role is truly full-time.
Adding a permanent AI executive means two recruitments, two fixed costs and two sets of single-person risk.
Accountable senior leadership, flexible capacity and a defined mandate that scales.
05 / FIVE PRACTICES
Provide accountable vCISO, vCAIO and board-level security leadership.
Explore practiceSecure, govern and monitor enterprise AI, from ISO 42001 readiness to red teaming.
Explore practiceBuild resilient security architecture, governance and operating capability.
Explore practiceTurning board intent into operating capability, evidence and measurable improvement.
Explore practiceYour people learn what we practise, in an Academy built as an institution.
Explore practiceEvery proposal names the people who do the work, before you sign anything.
Nobody is assigned after you sign. You know who leads your engagement before you commit.
Senior-led is structural, not aspirational: there is no junior rate card to staff from.
Steve Sharma's ASD IRAP endorsement, CISSP, CISM, CREST, SABSA, TOGAF and ISO/IEC 27001 Lead Auditor, each verifiable with its issuer.
Governance and technical security should not operate in separate silos. We connect executive governance, security architecture and technical assurance under one coordinated mandate.
| The question you'd ask | Large network | Specialist boutique | Platform / software | Cybersecurity Link |
|---|---|---|---|---|
| Who exactly does the work? | Varies by engagement | Varies by firm | Software | Named executive, before you sign |
| Security and AI governance? | Often separate teams | One or the other | Via software | Both, one firm |
| Can they secure what they govern? | Varies | Rarely | No | Yes, governance to red team |
| A fractional CISO and AI executive? | No | No | No | Yes, engaged as a pair |
| Prices before a sales call? | No | Sometimes | Yes | Fixed fee, shared on registration |
| Independent advice? | Often not | Usually | Vendor itself | Yes. No referral commissions, and we never recommend our own platform in our own assessments. |
| 24/7 monitoring and operations? | Yes | No | Yes | No. We do not run a security operations centre |
We put the last row in ourselves. If you need a SOC, we'll point you to one.
06 / THE TEAM
18+ years across four major banks, defence and government. Author, The CISO's AI Firewall.
15+ years leading enterprise risk, governance and compliance programmes across government and regulated sectors.
15+ years overseeing strategic talent management, workforce operations and administrative governance for technology enterprises.
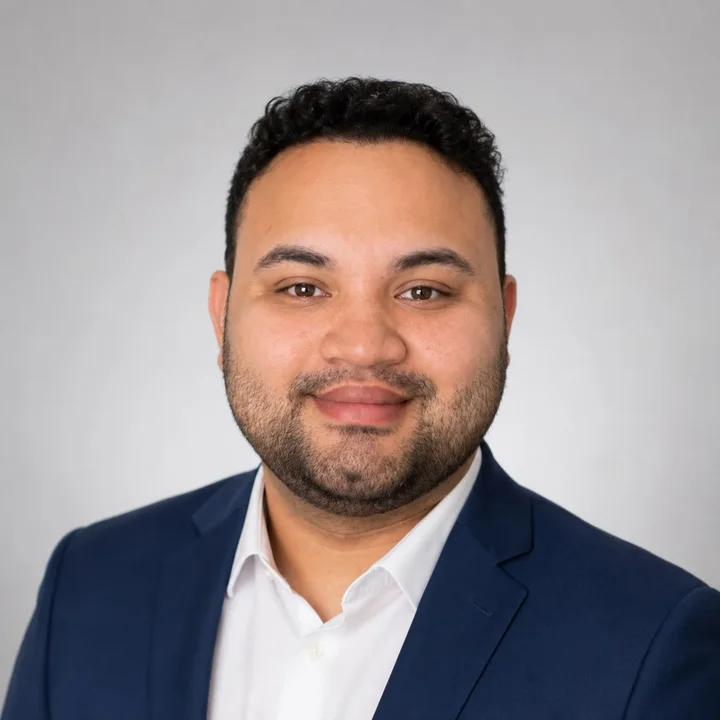
12+ years driving offshore service delivery, operational scaling and cross-border security engineering operations.
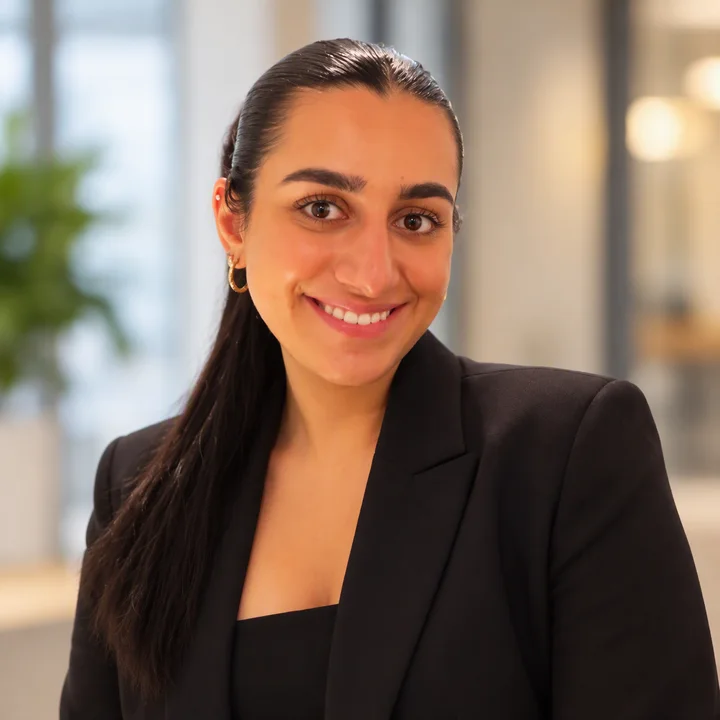
Specialist in emerging tech security, AI governance frameworks and cloud security architecture for modern enterprise environments.
HOW WE WORK
We work out whether we can help. Sometimes the answer is no.
What you have, what applies and what is exposed.
Scope, price, named executives and timeline.
The people named in the proposal do the work.
Controls undocumented, then evidenced to underwriter standard. Insurance renewal readiness improved.
INSURANCESecurity leader gone; interim executive in place. Audit findings moved into a structured remediation programme.
AUDITAI in three products, no governance. Certification readiness accelerated.
CERTIFICATIONOur engagements are covered by NDA. These success stories are anonymised by sector.
A senior executive takes the call, never a sales team.
07 / PRICING
Executive Advisory and Security Transformation are scoped in a discovery workshop, because the honest number depends on your size, exposure and obligations.
Full pricingSTART HERE
Fifteen questions, five minutes, your result on screen before we ask for anything. Nobody will chase you.
Take the assessmentA bounded, board-fundable first step with a written result you can take to your next meeting.
See the assessmentsA focused two-week engagement to identify the problem, establish priorities and produce an executive-ready action plan.
How the Sprint worksA named vCISO or vCAIO, on a fixed monthly fee, for as long as you need the seat filled.
Compare engagement models08 // Academy & Author Hub
Masterclasses for executives and courses for practitioners, taught by people who do this work. The aim is capability your people can use, not letters after a name.
A practical executive framework for securing, governing and deploying enterprise AI.
Insights
QUESTIONS WE GET ASKED
Choose a founder-led firm when you want to know who will do the work. We have traded since 2007, led by our founder, Steve Sharma. Every engagement is assigned a named senior executive before it begins.
The people named in your proposal do the work. No one is swapped in after you sign.
For enterprise-scale programmes, we provide the executive mandate. Where additional delivery capacity is required, we extend capability through our strategic partnership network, including our delivery partner Cyber Arista.
We build one: AISF, our AI Security Firewall. Our advisory stays product-neutral: AISF is never a condition of an engagement, and we don't recommend it as a finding in an assessment we perform.
Across different engagements, yes. On the same system, we stay independent.
Cost depends on the engagement. Fixed-scope entry points are listed on this page, with indicative fees for registered organisations. Executive Advisory is scoped in a discovery workshop.
Clear boundaries protect independent advice and make accountability easier to verify.
We prepare organisations for certification. The audit itself must be conducted by an accredited body.
We do not run a 24/7 security operations centre. If that is what you need, we will point you to someone who does.
We provide advisory and governance architecture, not legal advice.
On any system assessed under IRAP, we take one role: assessment or advisory. Never both. Assessment or AISF: where we assess a scope, we don't sell AISF into that same scope. 🚩 Steve to confirm this rule.
If the answer is “nobody, exactly,” that is worth a conversation.
hello@cybersecuritylink.com.auA senior executive replies. No sequences and no sales team.