
Founder & PrincipalSteve Sharma
IRAPCISSPCREST
18+ years across four major banks, defence and government. Author, The CISO's AI Firewall.
About Cybersecurity Link
Virtual CISO and Virtual Chief AI Officer leadership, with AI security, AI governance and cybersecurity assurance for enterprise, government and regulated organisations.
Cybersecurity Link is the trading name of SS Network Solutions Pty Ltd, ABN 66 124 215 970, founded in 2007 in Australia. Everything on this page is stated so you can check it.
5 named executives · 🚩14 register-linked credentials
Evidence before adjectives.
Every engagement lead named before signature
Meet them Register-linked credentials†14🚩[verify] Each linked to its issuing register
Verify Reference points05ISO/IEC 42001 · ISO/IEC 27001 · NIST AI RMF · OWASP LLM Top 10 · Essential Eight (AU)
See the map Engagements delivered†09Across four sectors; published with permission
See the work Founded†2007Australia · SS Network Solutions Pty Ltd · ABN 66 124 215 970
Entity detailsFor directors: go directly to what changed and who is accountable.
🚩 Credential count to confirm01 / WHY THE FIRM EXISTS
Almost every organisation now runs on it.
Security leaders inherited the responsibility without the budget, headcount or mandate, and still carry the exposure when something fails.
Between a large network, a single-discipline boutique and a governance platform sits a gap: a named executive who can govern AI and secure it, and who stays when the standard changes.
Cybersecurity Link exists to fill that gap and nothing else. Every engagement is led by a named senior executive. Every claim we make links to something you can check.
A founder-led practice, stated plainly.
I refocused this practice because I kept meeting the same person: a security leader handed AI on top of a full-time job, without budget, mandate or answers for the board.
This is a founder-led firm, and I would rather say that plainly than let you work it out. I am accountable for every engagement, and no engagement runs on me alone: each has a named executive and a published method. Where additional delivery capacity is required, we extend capability through our strategic partnership network. Cybersecurity Link has been trading since 2007, and I will not dress that up as more than it is. What I bring is more than 18 years across four major banks, defence and government, credentials that link to their registers, and a method published in full below.
Every engagement is assigned a named senior executive before the engagement begins. Where additional specialists are required, they are identified in the proposal and subject to client approval.
Founder & Principal
“Governing AI and securing AI are not the same discipline, and most organisations have only bought one.”
AI governance · AI security · board and executive advisory
18+ years across four major banks, defence and government. Author, The CISO's AI Firewall.
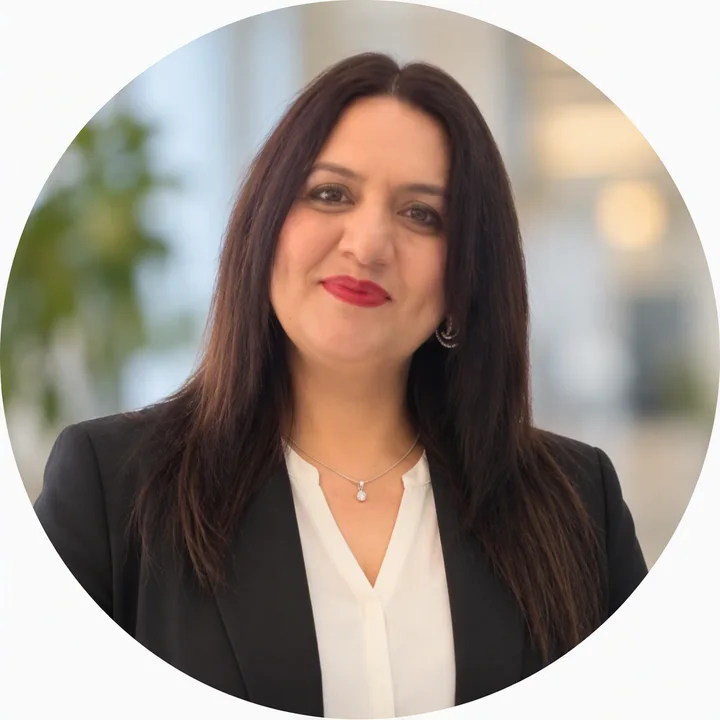
15+ years leading enterprise risk, governance and compliance programmes across government and regulated sectors.
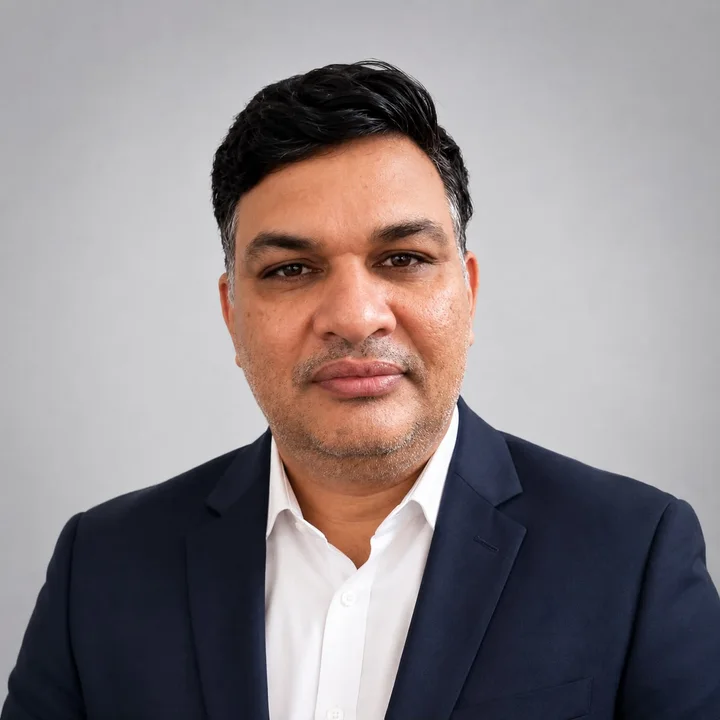
15+ years overseeing strategic talent management, workforce operations and administrative governance for technology enterprises.
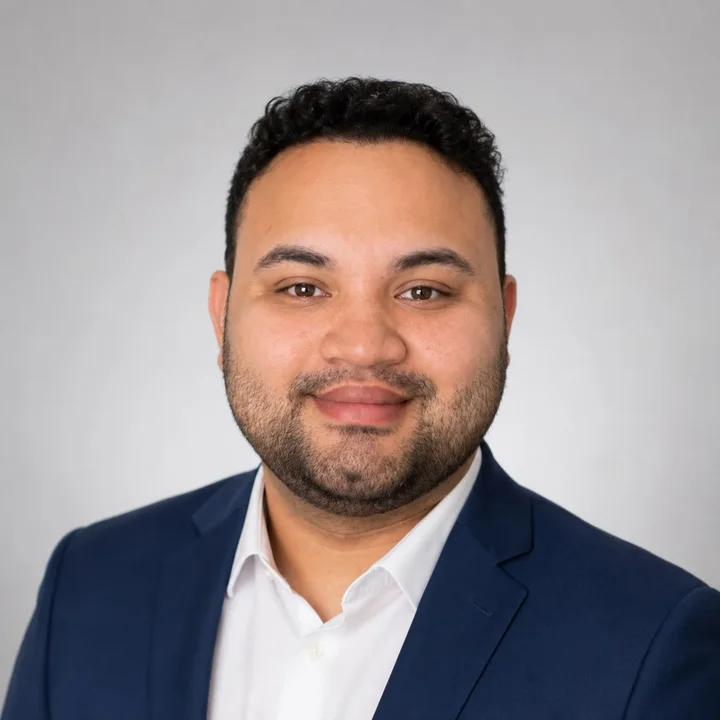
12+ years driving offshore service delivery, operational scaling and cross-border security engineering operations.
Specialist in emerging tech security, AI governance frameworks and cloud security architecture for modern enterprise environments.
Every engagement has a named lead. Where a second executive or specialist is needed, they are named in the proposal and subject to client approval. Decisions and evidence live in shared systems, not one person's head. Where additional delivery capacity is required, we extend capability through our strategic partnership network.
We build one governance system and map it, so a change to a standard updates the work instead of restarting it.
Every mapping is documented so an auditor can follow it. ISO/IEC 42001 and ISO/IEC 27001 are management-system standards; NIST AI RMF is a voluntary framework; OWASP LLM Top 10 is a technical resource; Australia's Essential Eight is evolving.
Assess what exists, what is deployed and what is actually governed.
Mapped control baseline, gap register and costed remediation sequence.
Design the governance architecture and technical controls together.
Governance system, control set, test procedures and board reporting pack.
The named executive leads, reports to leadership or the board, and maintains evidence.
Quarterly reporting, maintained evidence and standards-change notices.
Every engagement is designed for transfer to your own people.
Documented operating model and a named internal owner.
Each commitment includes the thing a buyer can use to test it.
Interchangeable resourcing works for large networks. Our model is different: the engagement lead is identified before work begins.
Product margin can make a recommendation worth less than it appears. Our advice is not funded by a vendor sale.
The same firm advising and then attesting creates a conflict, however carefully it is managed.
Credentials to their registers. Standards to their publishers. Regulatory statements to their source, dated and jurisdiction-labelled.
Each alternative is the right answer for someone. The useful question is where its advantage ends.
Scroll horizontally to compare
| Alternative | Genuinely better at | The gap | Cybersecurity Link |
|---|---|---|---|
| Large network | Multi-country scale and institutional comfort | The pitch team may not be the delivery team | Named executive in the proposal |
| Specialist boutique | Depth inside one discipline | The buyer owns the seams between disciplines | AI governance and AI security in one system |
| Governance platform | Speed and cost for a snapshot | A snapshot does not operate the programme | System, tests and named accountability |
| Permanent hire | Full attention and context | Time to hire, total cost and single-person risk | Capability now, transferred when ready |
| Do nothing | No cost when exposure is genuinely small | Exposure is often larger than it appears | A bounded assessment to establish which is true |
🚩 Challenge, approach and outcome to be supplied from a permissioned engagement, in wording the client has approved.
🚩 Outcome to be confirmed in writing by the client.
Security clients rarely want to be named, because a reference can read as admitting a past problem. Logos appear only with written permission. Clients who ask not to be named get the discretion we would give you.
🚩[Client quote] Published only with written permission and in the client's own words: no star ratings, stock portraits or edited sentiment.
Delivery, channel and professional association are different relationships. The page states which is which.
Cybersecurity Link provides the executive mandate and specialist security leadership. Where additional delivery capacity is required, we extend capability through our strategic partnership network, including Cyber Arista for delivery and technology hardware.
We do not take your clients direct.
Written into the partner agreement, not promised on a call. If your client approaches us independently, we tell you.
These are memberships and accreditations, not commercial partnerships. We receive no payment from any of them and none of them endorses us. Each name links to its source.
🚩[Association] · 🚩[Professional body]
No reseller agreements or referral commissions, and AISF is never a condition of an engagement.
We prepare organisations for certification; accredited bodies certify.
We don't run your SOC or monitor your environment around the clock.
If you need hands rather than leadership, we say so on the first call.
A fit decision should be possible before a sales conversation.
Enterprise, government and regulated organisations, roughly 200 to 5,000+ people, or any government entity
Boards carrying accountability they cannot delegate
AI adoption ahead of governance
Teams that want the capability handed over, not held
Organisations under roughly 200 people, where the economics rarely work
Teams needing hands-on implementation rather than executive leadership
Buyers seeking a certificate without the system
Buyers looking only for the cheapest compliance tick
Outside that fit? Say so on the first call. We will point you toward a more appropriate firm and take nothing for the referral.
Most of what a procurement or vendor-risk team asks is below. The full supplier pack is available on request.
Email 🚩procurement@cybersecuritylink.com.au. We reply personally, usually within one business day.
🚩 Mailbox to confirmEverything on this page is checkable. If something is not, tell us and we will fix it. To test the thinking before the firm, start with the writing.
45 minutes · with Steve, not a salesperson · no obligation, no follow-up sequence