Not a consultant.
A consultant advises. A vCAIO accepts executive accountability for the AI agenda, drives decisions and reports to leadership and the board.
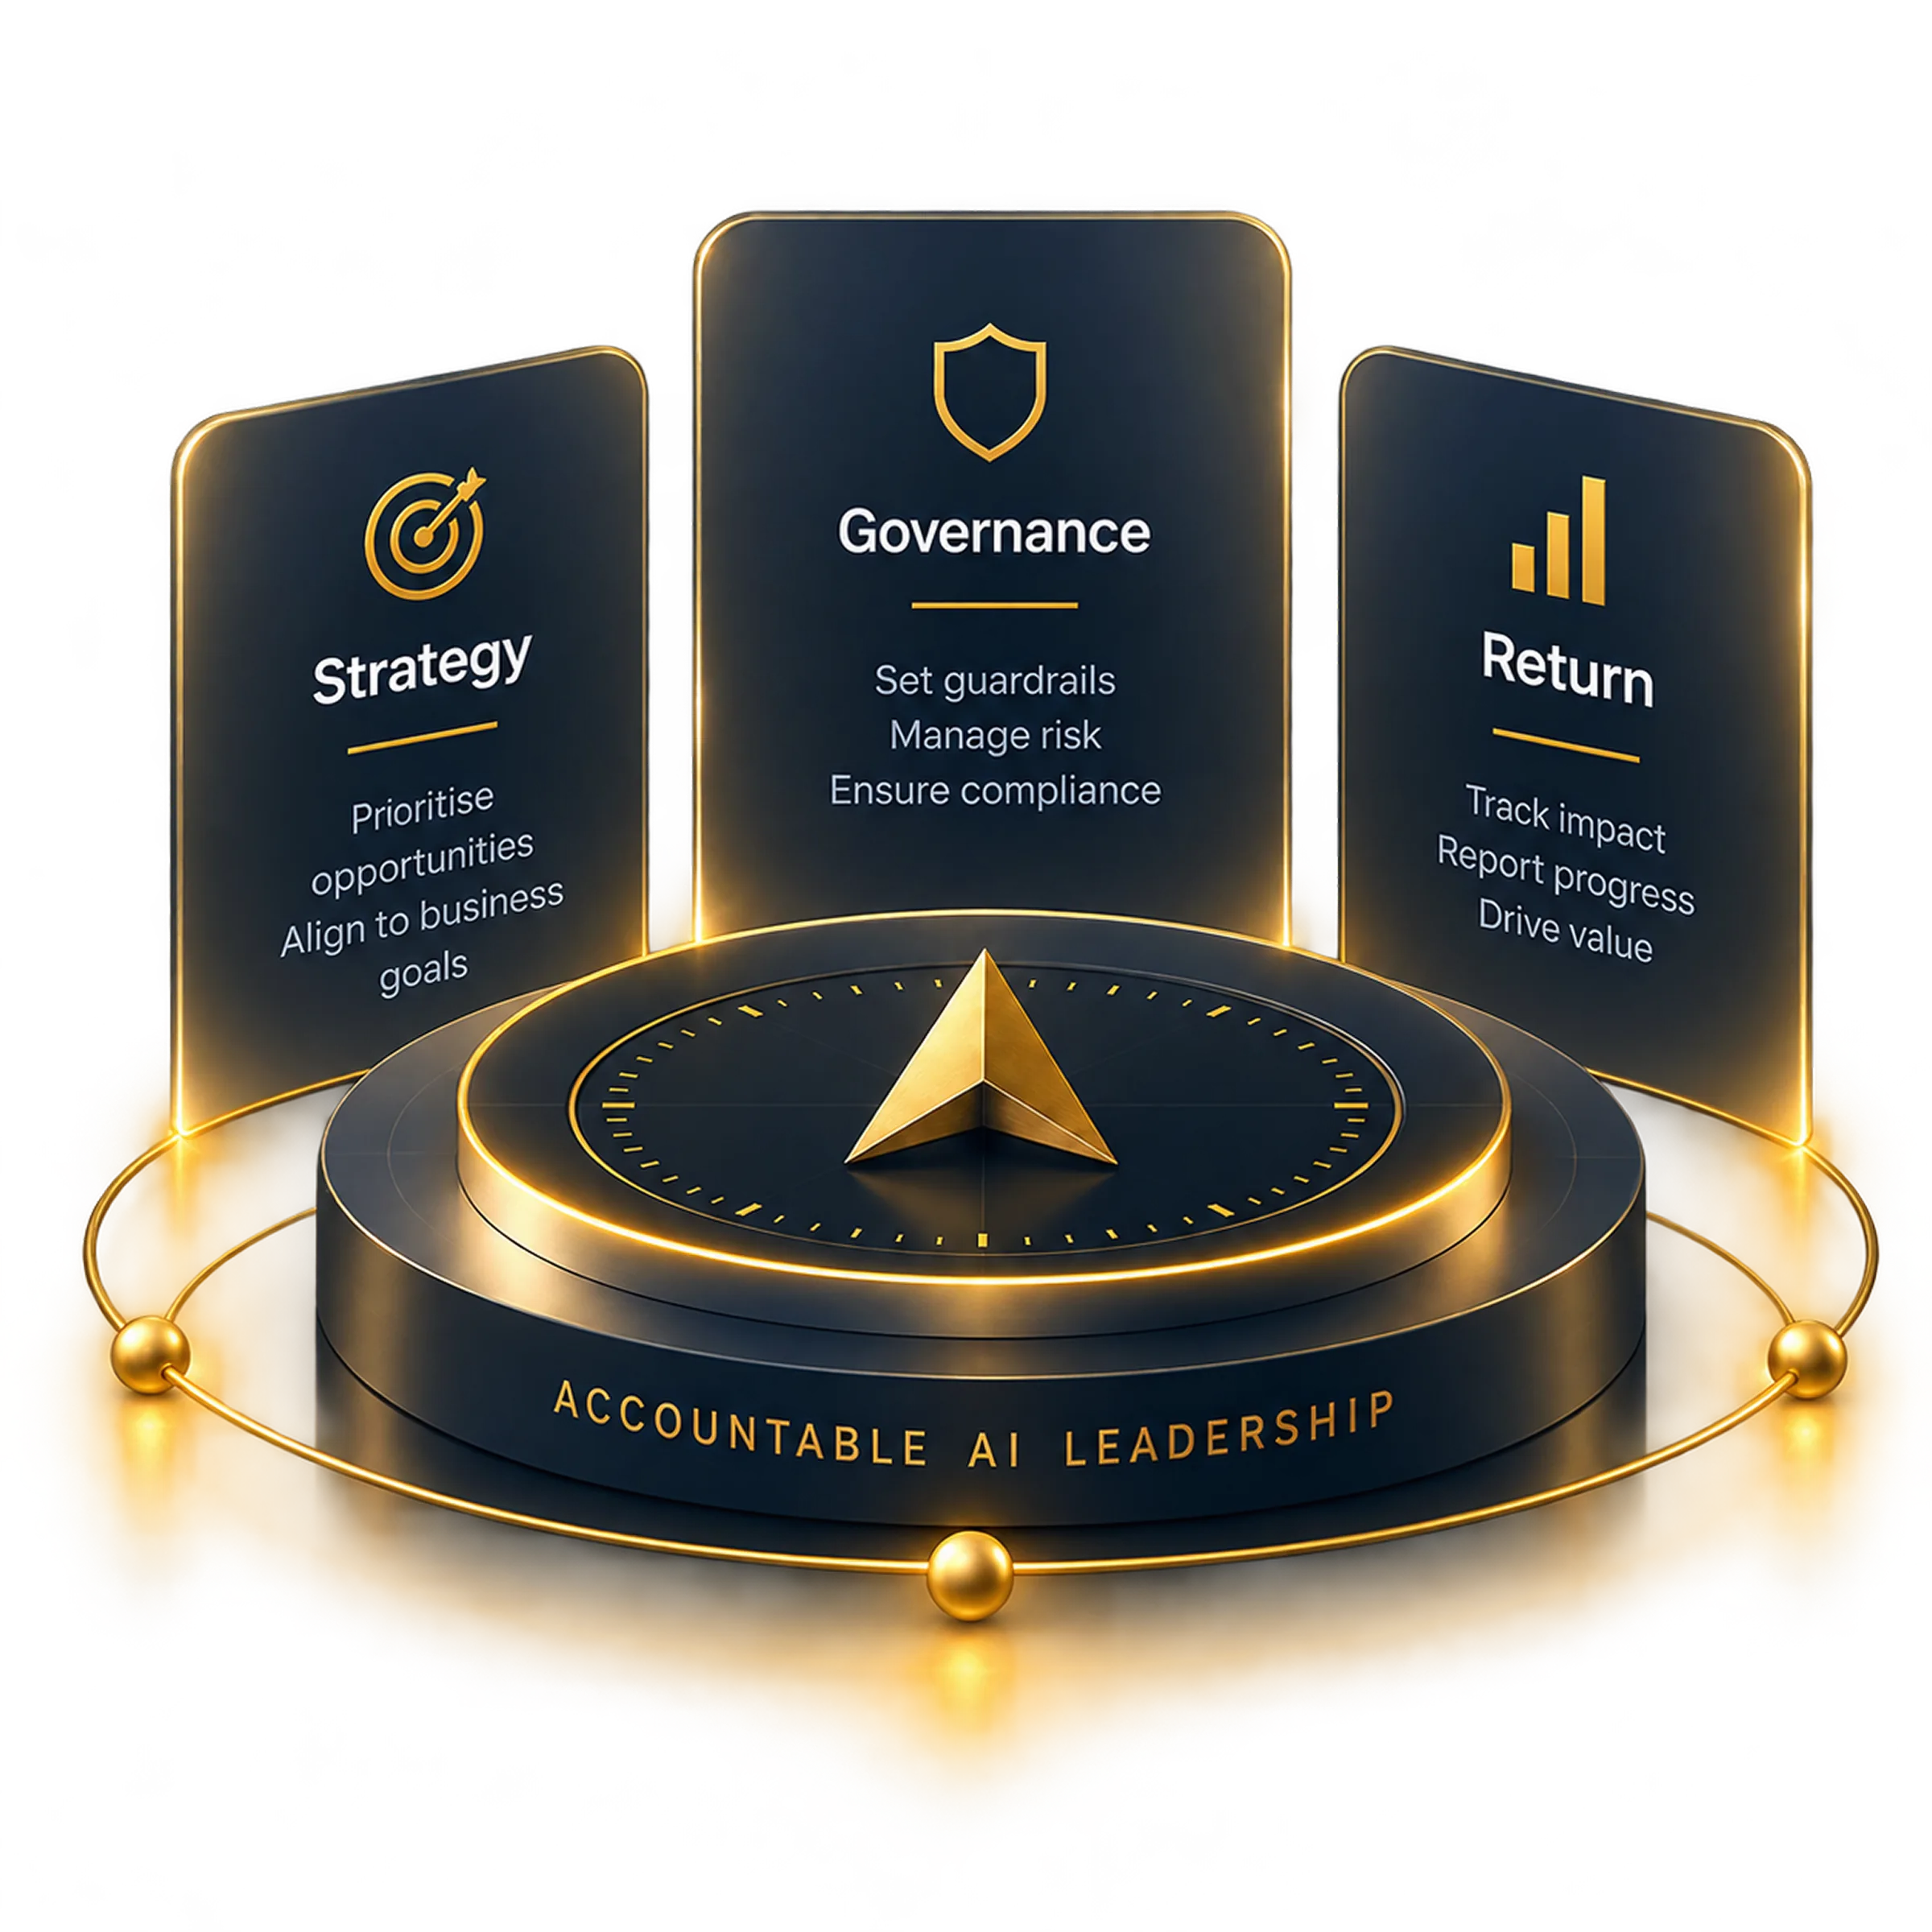
A Virtual Chief AI Officer (vCAIO) provides accountable leadership across AI strategy, governance, risk, security and executive reporting, without requiring a permanent C-suite appointment.
Need broader enterprise security leadership? Our vCISO service provides accountable security strategy, risk, compliance and board leadership. Explore vCISO →
Led by the author of The CISO's AI Firewall · ISO/IEC 27001 Lead Auditor · Senior-led delivery on every engagement
Author, The CISO's AI Firewall · 18 years across four major banks, defence and government
A senior executive, appointed on a fractional basis, who owns your AI strategy, governance, risk, security and board reporting.
Organisations with AI in use and nobody accountable for it. Typically 200 to 5,000 people, or any regulated or government entity.
Register to see indicative fees. A fixed monthly fee, confirmed in writing after scoping, instead of a permanent C-suite salary.
The 90-Day AI Leadership Gate, with outcomes agreed in writing before we begin.
At day 90 you continue, change scope, or stop. No exit fee, no notice period on that decision.
We govern AI and secure it, and we provide a vCISO alongside the vCAIO. Led by the author of The CISO's AI Firewall.
Pilots produce demos but not the business value that justified them, and nobody owns the decision to scale them or stop them.
AI projects get approved on ROI projections that nobody measures after launch. Finance stops sponsoring and starts saying no.
The board approves major AI investment and moves on. Governance expectations go unset, and AI risk never reaches a standing agenda.
Organisations that suspect or have evidence of staff using prohibited public GenAI tools. If nobody owns AI, nobody knows which tools those are or what data they touch.
Source: Gartner survey of 302 cybersecurity leaders, March to May 2025.AI doesn't need another project manager. It needs an accountable executive.
Cybersecurity Link provides fractional AI leadership across strategy, governance, risk, security and board reporting, connecting AI ambition to accountable execution.
A Virtual Chief AI Officer (vCAIO) is a senior executive appointed on a fractional basis to provide accountable leadership across AI strategy, governance, risk, security and board reporting, with the authority to decide what gets built, what gets stopped and what gets governed. The role complements your existing leadership team without a permanent C-suite appointment. Unlike a consultant, a vCAIO holds the accountability rather than advising on it.
A consultant advises. A vCAIO accepts executive accountability for the AI agenda, drives decisions and reports to leadership and the board.
Giving AI accountability to your CTO dilutes their focus and still leaves the specialist gap. They should be your closest partner, not your AI owner.
We don't fine-tune models, write pipelines or configure your data platform. We decide what gets built and hold whoever builds it to standard.
Software produces a dashboard. A dashboard cannot chair your AI forum or answer for a decision.
We sell no models and resell no third-party licences or seats. Our own platform, AISF, is never a condition of an engagement and never a finding in our own assessments.
This role sits alongside your CIO, CTO and CISO, not above them. If you already have a security or technology leader, this is the person who takes AI off their plate and gives them back their day job. If they would rather keep AI and want executive backup instead, that works too. We'll say which we think fits on the call.
The AI strategy, roadmap and governance model, re-cut as the market moves
Which use cases get funded, and which get stopped
Your AI governance forum: chaired, minuted, decisions recorded
The AI inventory: what you're running, who owns it, what it touches
Model, vendor and third-party AI risk, including the AI inside software you already bought
AI security controls: tested, not assumed
Board and executive reporting on progress and return
Regulatory position across the frameworks that apply to you
Paid in full, whatever the workload.
AI cost sits in seat licences, usage fees and features inside software you already bought. Until someone counts it, nobody knows the total.
A permanent Chief AI Officer means a full-time salary and a new standing function. We give you senior ownership from day one, and a governance system your team ends up running.
Engagement fees are scoped according to organisational size, regulatory exposure, mandate and reporting requirements.
Your named executive, the AI inventory, governance framework and first board report.
Full scope and pricingEverything in Establish, plus the operating model, third-party AI risk, tested security controls and quarterly executive reporting.
Full scope and pricingEverything in Govern, plus forum chairing, board attendance, investment governance and multi-jurisdiction position.
Full scope and pricingA short scoping conversation, with no charge and no obligation.
A written proposal naming your executives, your scope and your fee.
Fixed monthly fee. No hourly billing, and no change orders for work inside the agreed scope.
Fixed fee, agreed scope, no surprises.
Request an indicative scopeEvery engagement runs to the 90-Day AI Leadership Gate, with outcomes agreed in writing before we start. At day 90 you decide: continue, change scope, or stop.
We do this because many organisations reading this have already funded AI work that didn't deliver. You shouldn't have to take our word for it either.
No notice periodNo exit feeNo argument
Select a column to compare it with us.
| The question you'd ask | Full-time CAIO | Give it to your CTO | AI consultancy | Governance platform | Cybersecurity Link |
|---|---|---|---|---|---|
| Time to start | Months | Immediate | Weeks | Days | Days |
| Owns the outcome | Yes | In addition to their day job | No, advises | No, reports | Yes, named |
| Cost | Full salary | Hidden: their focus | Project fees | Licence + services | Fixed fee, shared on registration |
| Can secure the AI, not just govern it | Depends on the hire | Rarely | Rarely | No | Yes, both |
| Independent of AI vendors | Yes | Yes | Often partnered | Is the vendor | Yes, contractually |
| Builds your internal capability | Yes | No | Rarely | No | Yes, that's graduation |
| Hands-on model and pipeline work | Yes | Yes | Yes | N/A | No: we direct, others build |
We put the last row in ourselves. A vCAIO decides what gets built and holds it to standard. The building is a separate job, and we'll tell you who should do it.
Each solves a different problem. The tier describes your situation, not the quality of the service. You can move between tiers as your AI exposure and internal capability change.
“We have AI everywhere and nobody owns it.”
Not included: model development, platform engineering, certification audit
See what Establish costs“We have to prove it's governed.”
Not included: the certification audit itself, 24/7 monitoring
See what Govern costs“AI is core to what we sell.”
Not included: model development; assessment of systems we advise on
See what Lead costsNot sure which one fits? We'll help you work out which engagement suits your situation. If the honest answer is a full-time hire, we'll tell you that too.
Request an indicative scopeTHE TEAM

18+ years across four major banks, defence and government. Author, The CISO's AI Firewall.
15+ years leading enterprise risk, governance and compliance programmes across government and regulated sectors.
15+ years overseeing strategic talent management, workforce operations and administrative governance for technology enterprises.
12+ years driving offshore service delivery, operational scaling and cross-border security engineering operations.
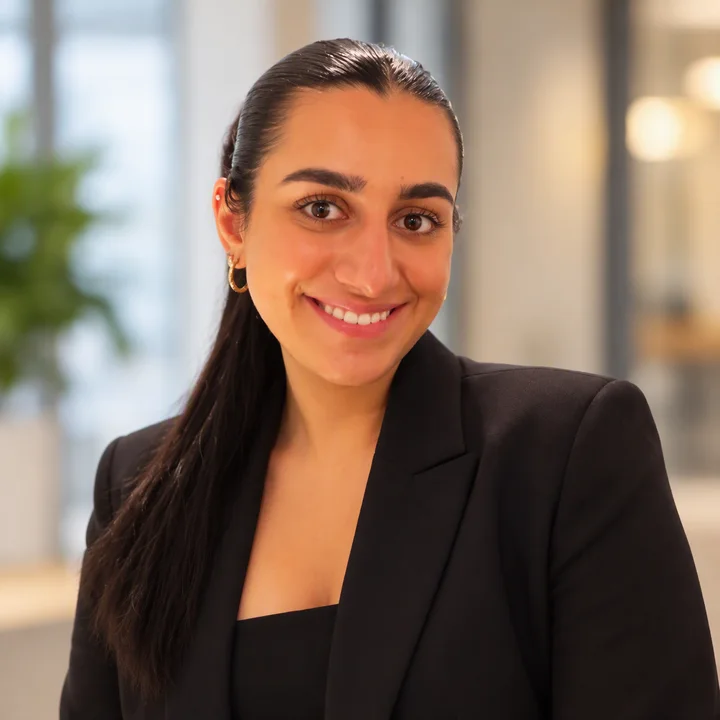
Specialist in emerging tech security, AI governance frameworks and cloud security architecture for modern enterprise environments.
Because AI governance is a management-system discipline, the EU AI Act sets cybersecurity requirements for high-risk systems, and unapproved AI use is a security exposure as well as a governance gap. Three answers you can check yourself.
ISO/IEC 42001 shares its management-system structure with ISO/IEC 27001: leadership, internal audit, management review and corrective action. Our founder is an ISO/IEC 27001 Lead Auditor.
ISO/IEC 42001:2023 · ISO/IEC 27001:2022Article 15 sets accuracy and cybersecurity requirements for high-risk AI systems. Where it applies to your system and role, meeting it takes security testing, not policy alone.
EU AI Act · Art. 15A substantial proportion of executives report concerns about data exposure through unapproved AI use. Shared agent packages have performed data exfiltration and prompt injection without users noticing. Shadow AI is a governance problem and a security incident. Firms that only write policy find out about the second one late.
Governing AI without being able to secure it is half an answer. We do both, and we codified the approach in The CISO's AI Firewall: a practical executive framework for securing, governing and deploying enterprise AI. The method behind our AI leadership:
We call it the 90-Day AI Leadership Gate. The first 90 days establish the initial operating position, with outcomes agreed in writing before we begin. It's the part you can hold us to first.
Access to systems, policies and people using AI, a sponsor who can unblock decisions, and a few hours each month for interviews and review. We write every required document.
Governance moves from establishment to operation and assurance as your team takes over. We stay only at the level you still need. The intended outcome is that you graduate to a lower tier.
They do different jobs: values, risk management, a management system, legal obligation and technical security. Here's how they fit together.
If you already operate an ISO 27001 management system, existing governance, documentation and improvement processes may provide a strong foundation for ISO/IEC 42001. If your exposure is mostly US, start with NIST AI RMF. Where the EU AI Act applies, its obligations set your floor wherever you start.
AI management system
Voluntary framework
LLM security resource
Role-based obligations
National guidance
Risk-proportional oversight
Supervisory model governance
Data protection obligations
Where your obligations fall outside this list we'll tell you, and where they turn on legal interpretation we work alongside your counsel.
A senior executive takes the call. If a full-time hire is the right answer for you, we'll say so on that call.
Our engagements are covered by NDA. These success stories are anonymised by sector.
Success stories are anonymised by sector and covered by NDA. Each is published only with client permission.
Staff had adopted AI across the business with no inventory, no policy and no record of what customer data was involved. We built the inventory, established governance and named ownership, and gave the board a complete picture for the first time. Some tools were retired, others re-scoped, and the rest now run under documented ownership.
Read the story
🚩[Client quote to supply, with written permission]
🚩[Second client quote, with written permission]
The 90-day milestone is the initial commitment. After that there's no minimum term and no annual lock-in.
Stated in the engagement letter, not buried in it. The same notice applies to us. At the day-90 gate, no notice is required at all.
Everything we build is yours: the inventory, the framework, the policy set and the evidence. If you hire a permanent Chief AI Officer, we brief them and help you interview.
Named executives in the proposal, a fixed monthly fee and no change orders for work inside the agreed scope. Where additional delivery capacity is required, we extend capability through our strategic partnership network, including our delivery partner Cyber Arista. We disclose that in writing before you sign.
We don't sell AI. No models, no platforms, no licences, no referral fees. We hold no vendor partnerships, and we'll tell you when a tool you already own is good enough.
We don't build the models. No fine-tuning, no pipeline engineering, no MLOps. We decide what gets built and hold whoever builds it to standard: your team, your integrator, or our delivery partner Cyber Arista, disclosed in writing.
We prepare you for certification. We don't certify our own work. ISO/IEC 42001 certification comes from an independent certification body. Where independence matters, assessment and advisory roles are separated.
We provide governance architecture, not legal advice. Where your obligations turn on the interpretation of a specific jurisdiction's law, we work alongside your counsel.
And governance is designed to help, not obstruct. If our framework slows your teams down, we've built it wrong and we'll fix it. Controls that get bypassed aren't controls.
Govern and Lead, where scoped.
Everything we do.
So your people can run what we build.
Need broader enterprise security leadership? Our vCISO service provides accountable security strategy, risk, compliance and board leadership. AI risk and cyber risk are one board conversation, so we provide both executives, cross-briefed under one contract and one governance architecture.
A 🚩[N]-page briefing for boards. No technical knowledge assumed.
ANALYSISISO/IEC 42001, NIST AI RMF and the EU AI Act: what each one does, and where to start.
REFERENCEPlain-English definitions of every standard on this page, jurisdiction-labelled and dated.
23 // FAQ
We lead your AI agenda because AI governance and AI security are one problem. ISO/IEC 42001 uses the same management-system structure as ISO/IEC 27001. Our founder is an ISO/IEC 27001 Lead Auditor. Where the EU AI Act applies, high-risk systems must meet cybersecurity requirements.
If AI is already being used across your organisation, the next question is accountability. Cybersecurity Link provides named, fractional AI executive leadership across strategy, governance, risk, security and board reporting.
Book a confidential strategy sessionOr write to us directly: hello@cybersecuritylink.com.auA senior executive replies, usually within one business day. We'll assess whether a vCAIO is the right model, and tell you if a different approach would be better.
A short brief: the accountability gap, the options, what each costs, and the questions your executive team will ask. Written to be forwarded.
Who's accountable for AI? A 🚩[N]-page briefing for boards. No technical knowledge assumed.
One page: what AI governance costs, what ungoverned AI costs, and how to measure whether it worked.